
Description
Complete Digital Investigation Kit | Mobile, Windows & Media Evidence
Multi-Source Digital Investigation, Data Recovery & Evidence Processing Toolkit
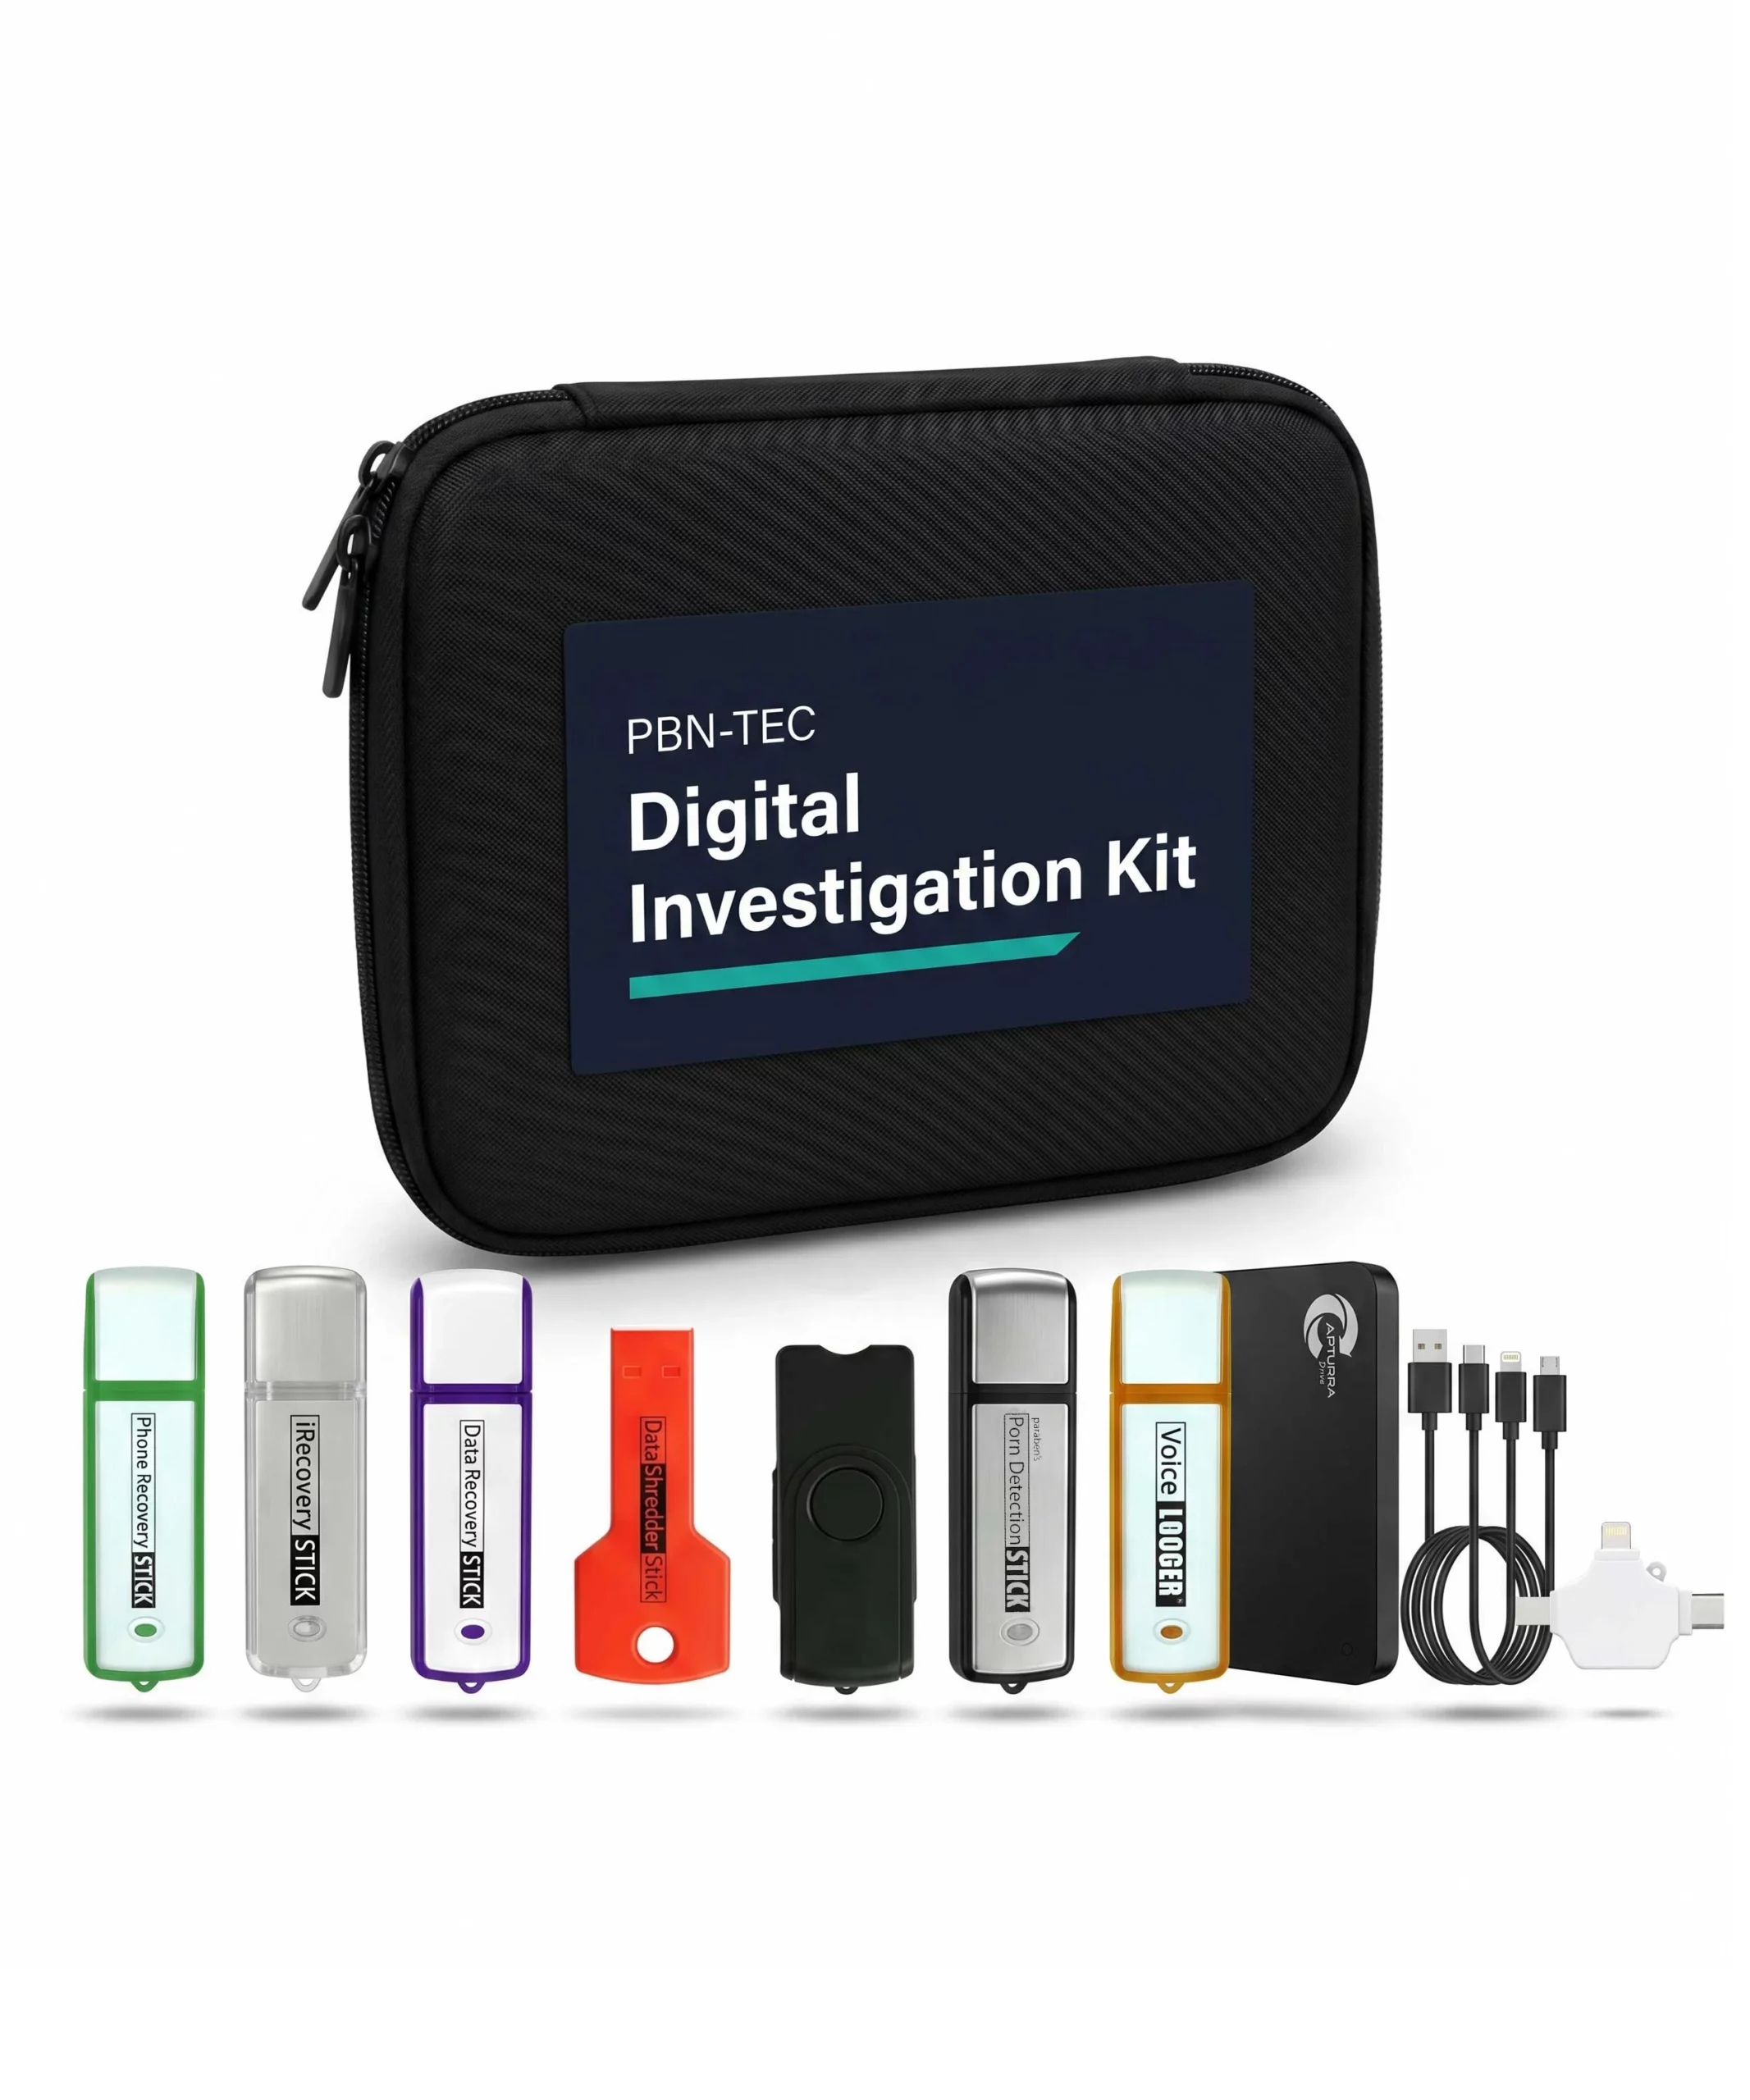
The Complete Digital Investigation Kit is a portable toolkit for authorized investigations involving mobile devices, SIM/UICC cards, Windows computers and digital media.
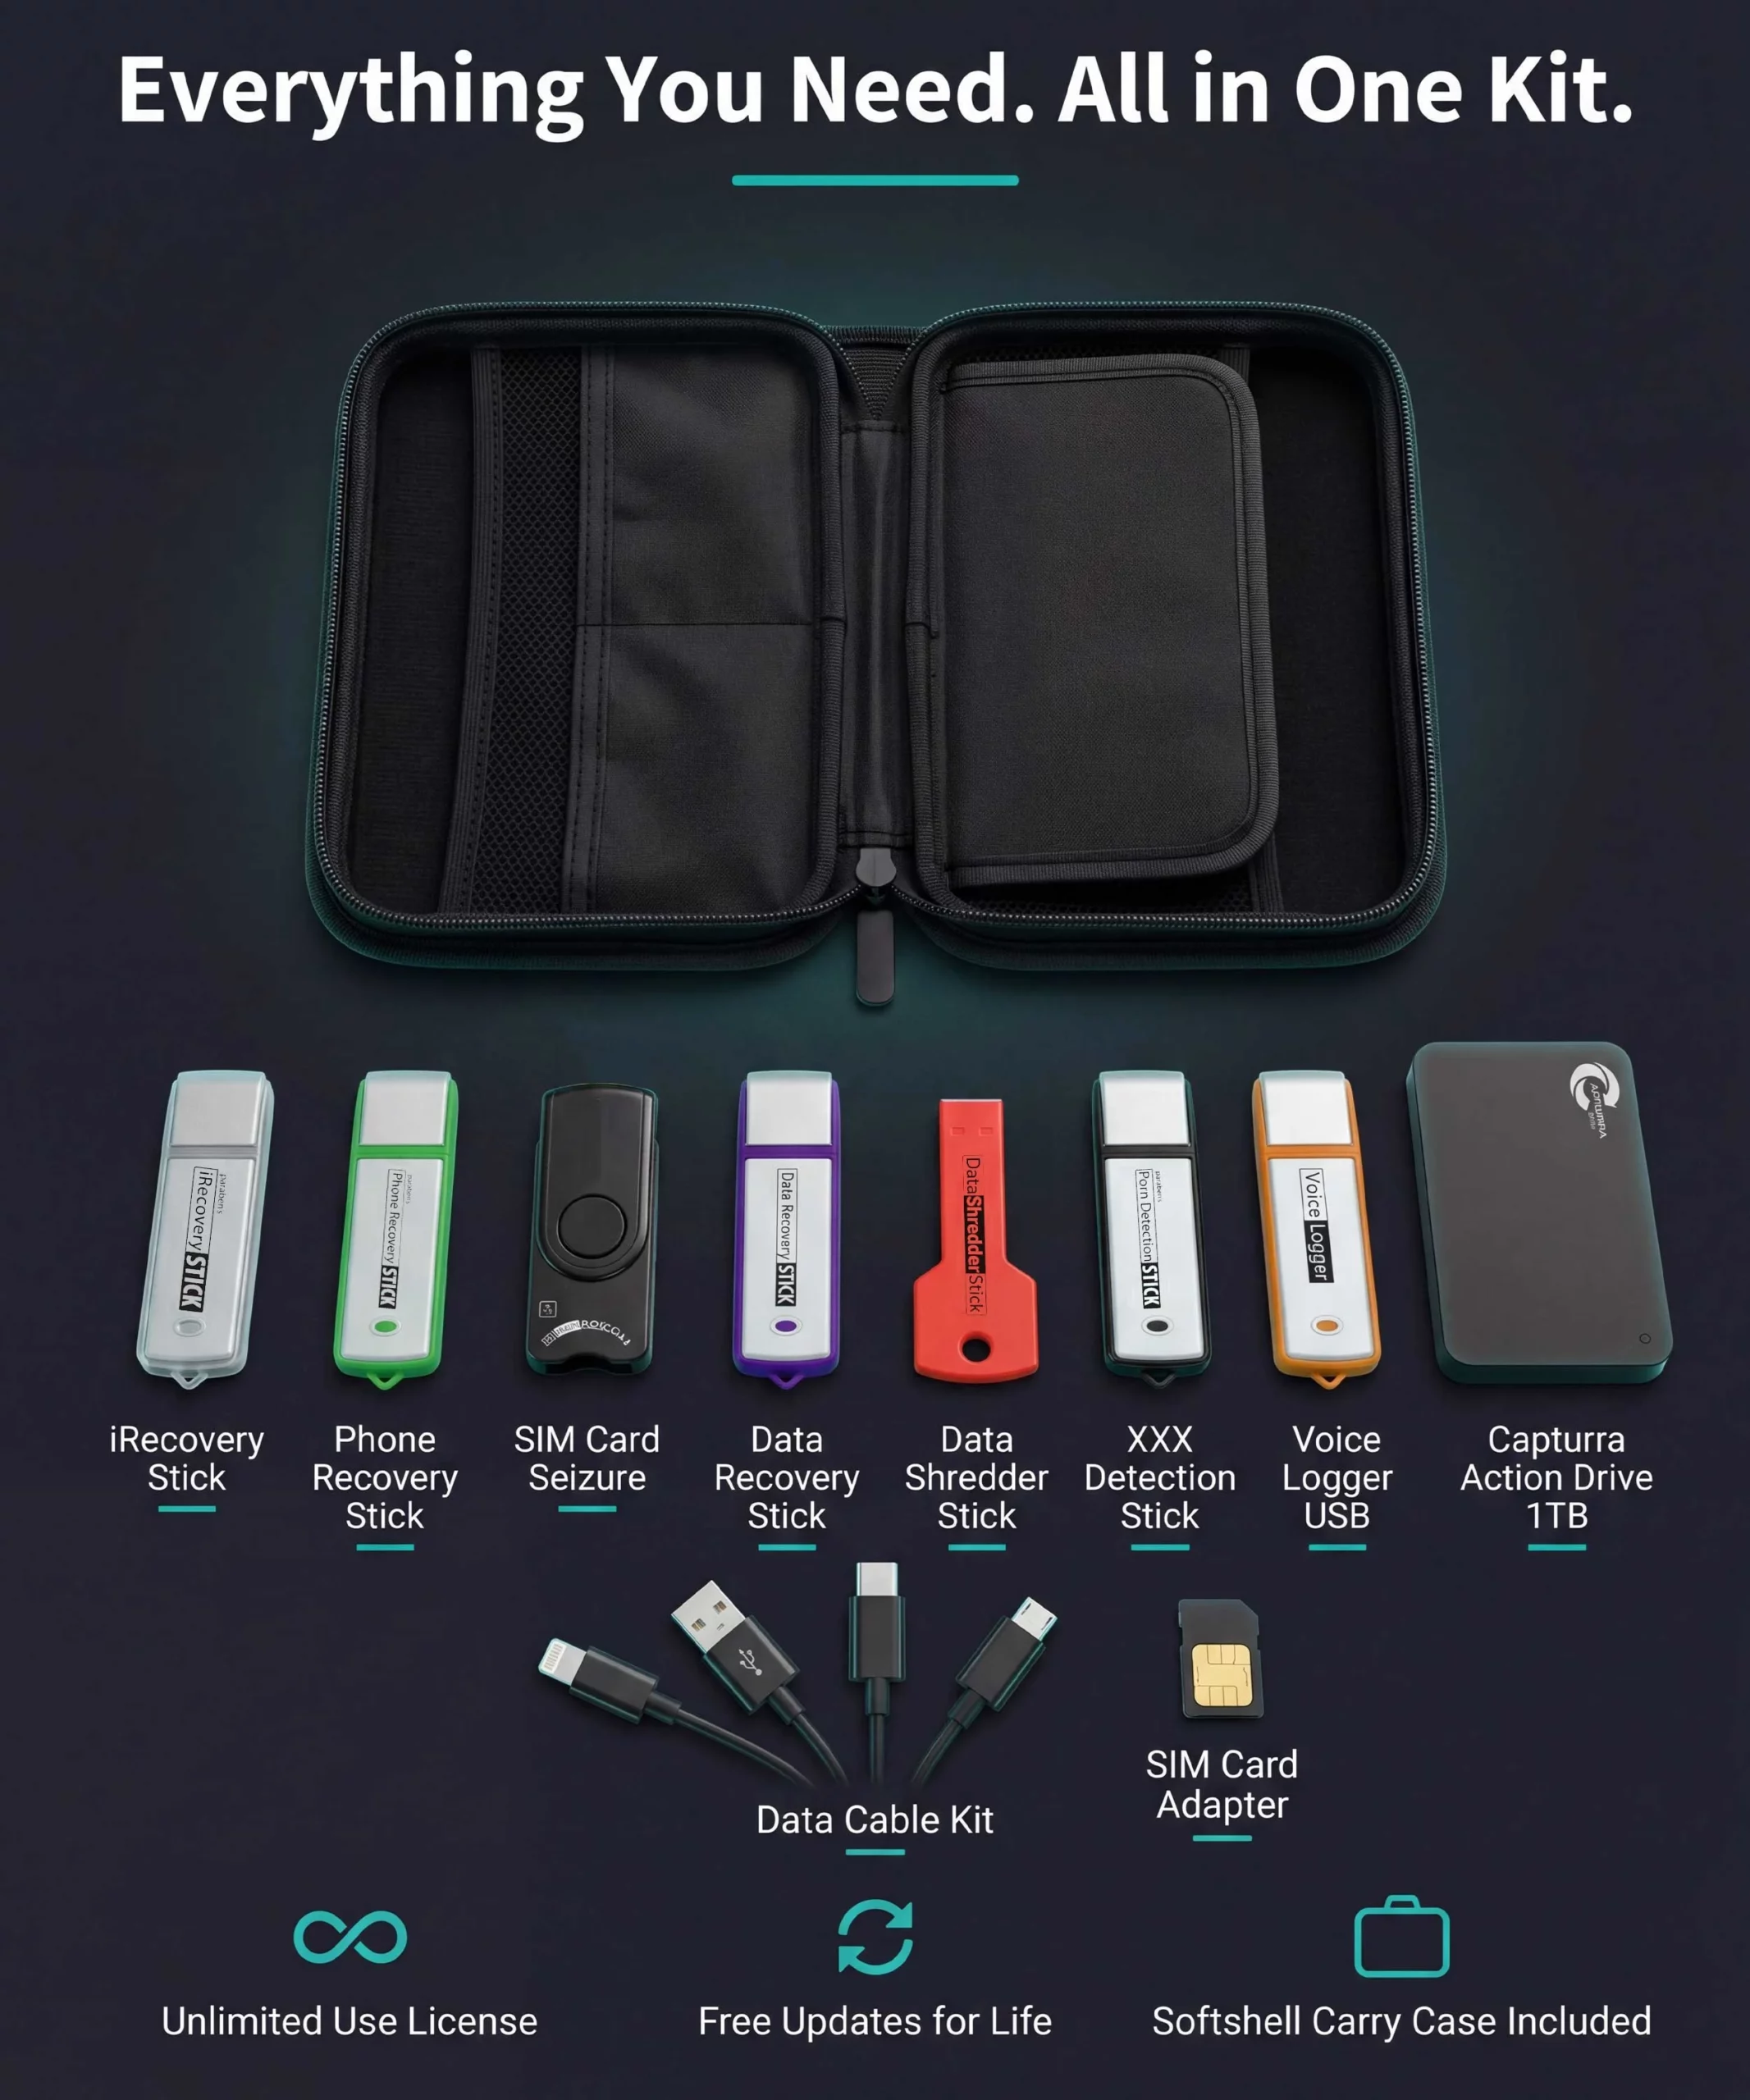
It brings together platform-specific tools for mobile data extraction, SIM evidence examination, Windows data recovery, digital media duplication, content screening and audio investigation within one portable case.
Rather than treating digital investigation as a single-device workflow, the kit supports multiple evidence sources through dedicated tools selected according to the investigation objective and accessible data source.
Digital Investigation & Evidence Collection Technology
Primary Category: Digital Investigation & Evidence Collection Technology
Secondary Categories:
- Mobile Device Investigation & Data Extraction
- Computer Data Recovery
- Digital Media Duplication & Evidence Offloading
- Explicit Content Detection & Digital Media Review
- SIM / UICC Evidence Investigation
- Windows Audio Monitoring & Recording
Primary Function: Multi-Source Digital Data Extraction, Recovery, Duplication, Media Review & Evidence Processing
Evidence Sources: iPhone / iPad, Android smartphones and tablets, SIM / UICC cards, Windows computers, removable storage, digital photographs and video, and accessible surveillance or recording media.
Product Type: Portable Multi-Tool Digital Investigation & Evidence Processing Kit
Mobile Device Investigation & Data Extraction
The kit includes dedicated tools for supported iPhone/iPad and Android investigations, allowing investigators to work with accessible device data through platform-specific extraction workflows.
Typical investigation objectives include:
- Mobile data extraction
- Smartphone investigation
- iPhone data extraction
- Android data extraction
- Mobile artifact extraction
- Mobile evidence collection
- Review of communications, contacts, multimedia and other supported artifacts
- Export and organization of extracted investigation data
The available data depends on the device, operating system, security state, software compatibility and access conditions.
iPhone & iPad Investigation
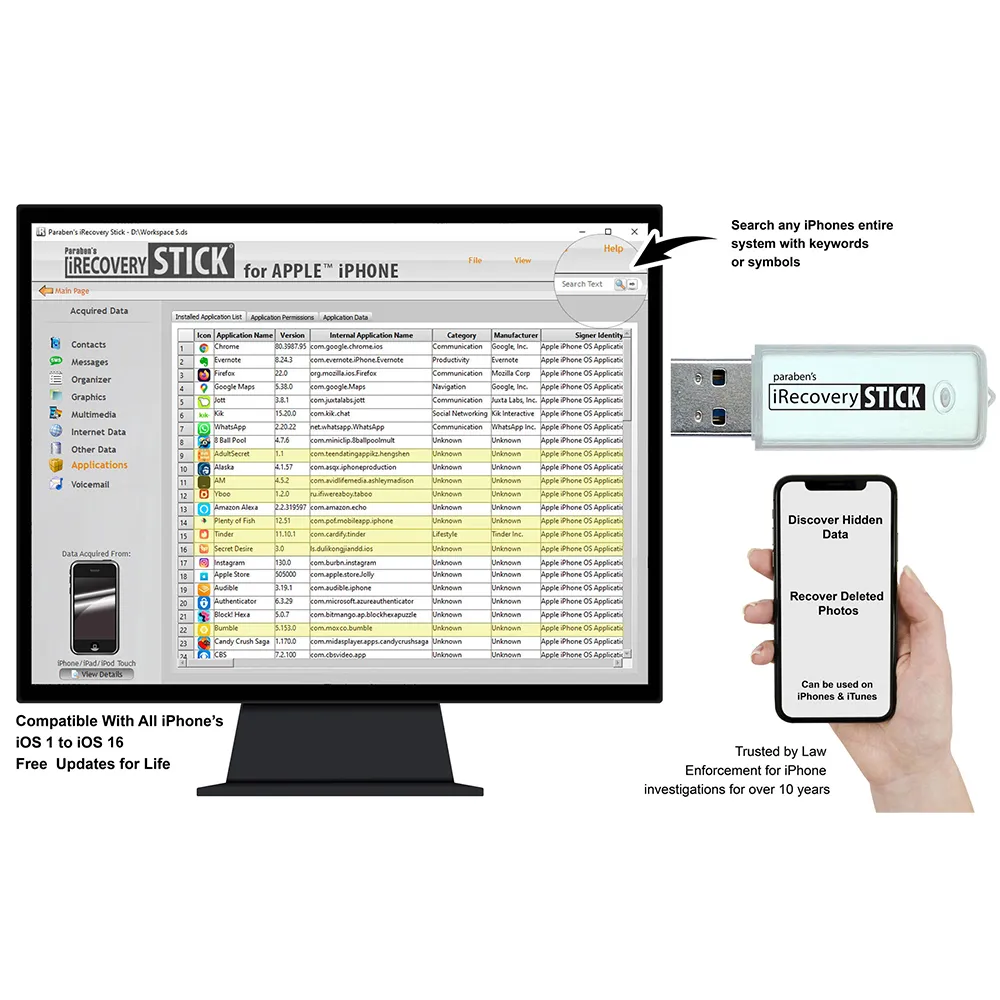
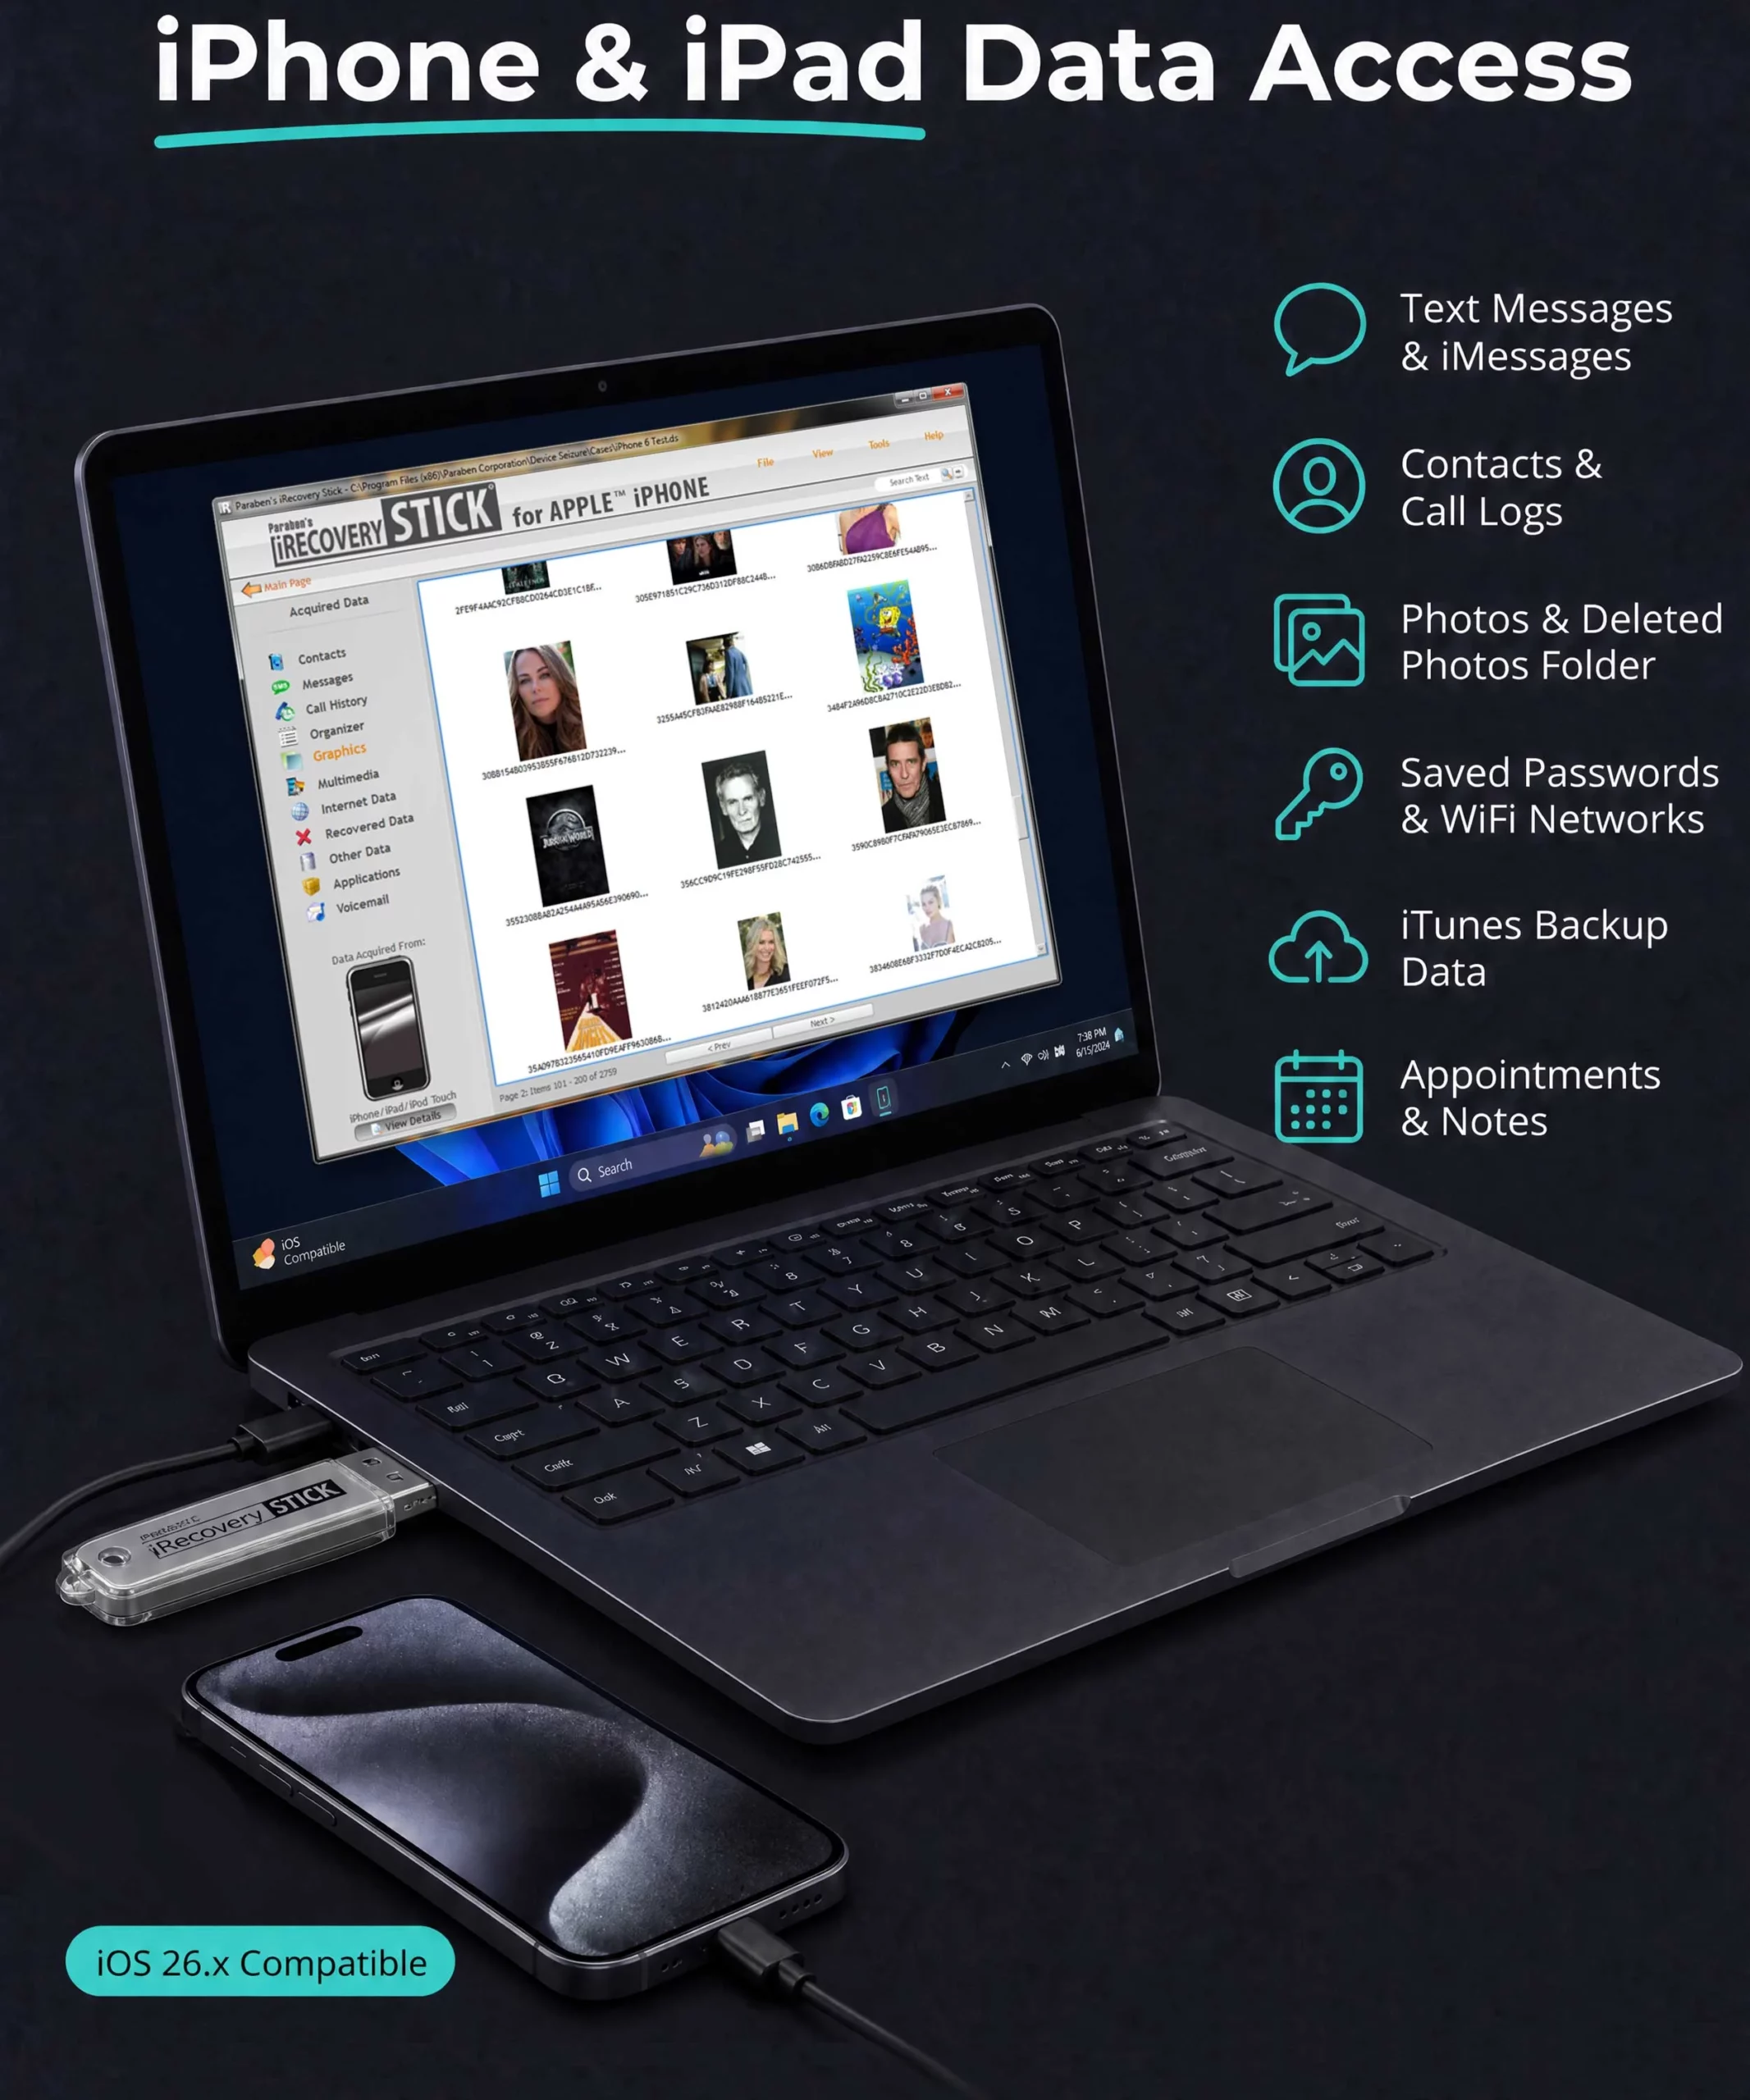
The iRecovery Stick provides a dedicated environment for supported iPhone, iPad and iPod touch data extraction.
Current manufacturer documentation specifies support for iOS 16.x and below. Device and software compatibility should therefore be verified before an investigation.
Android Investigation
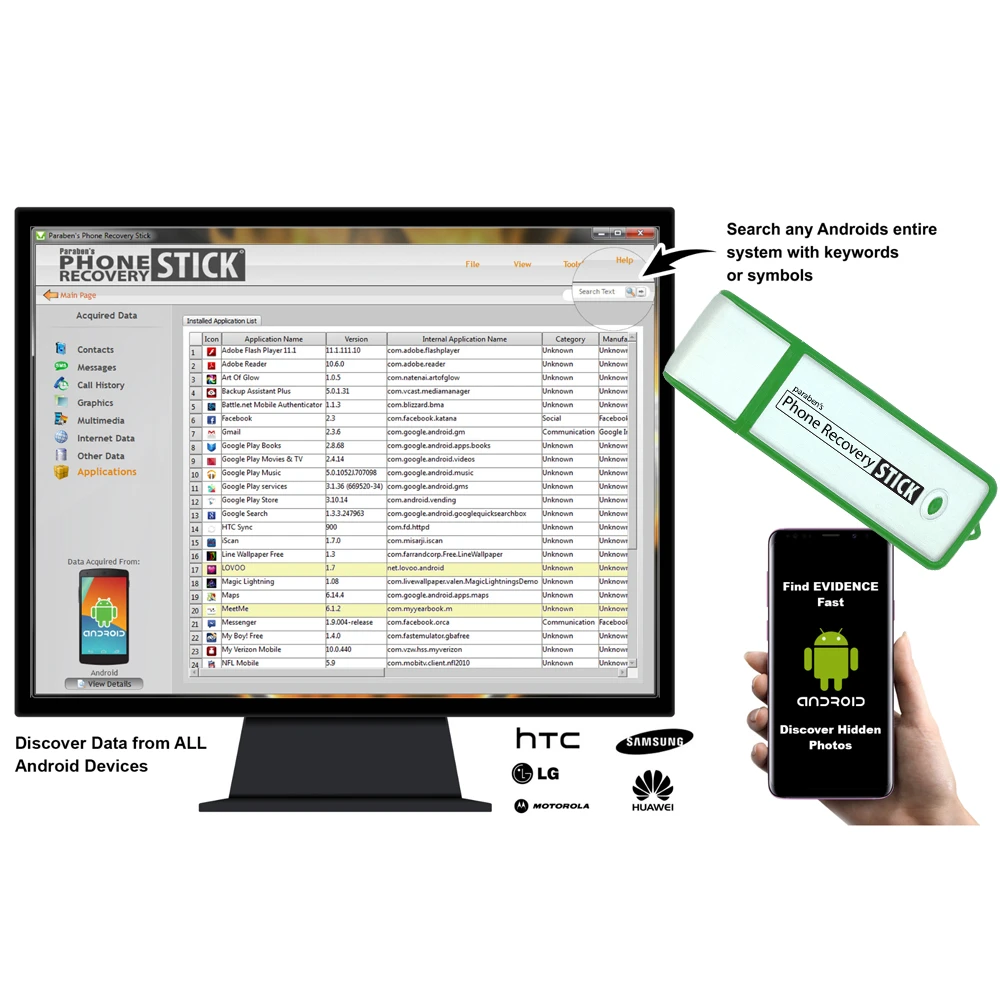
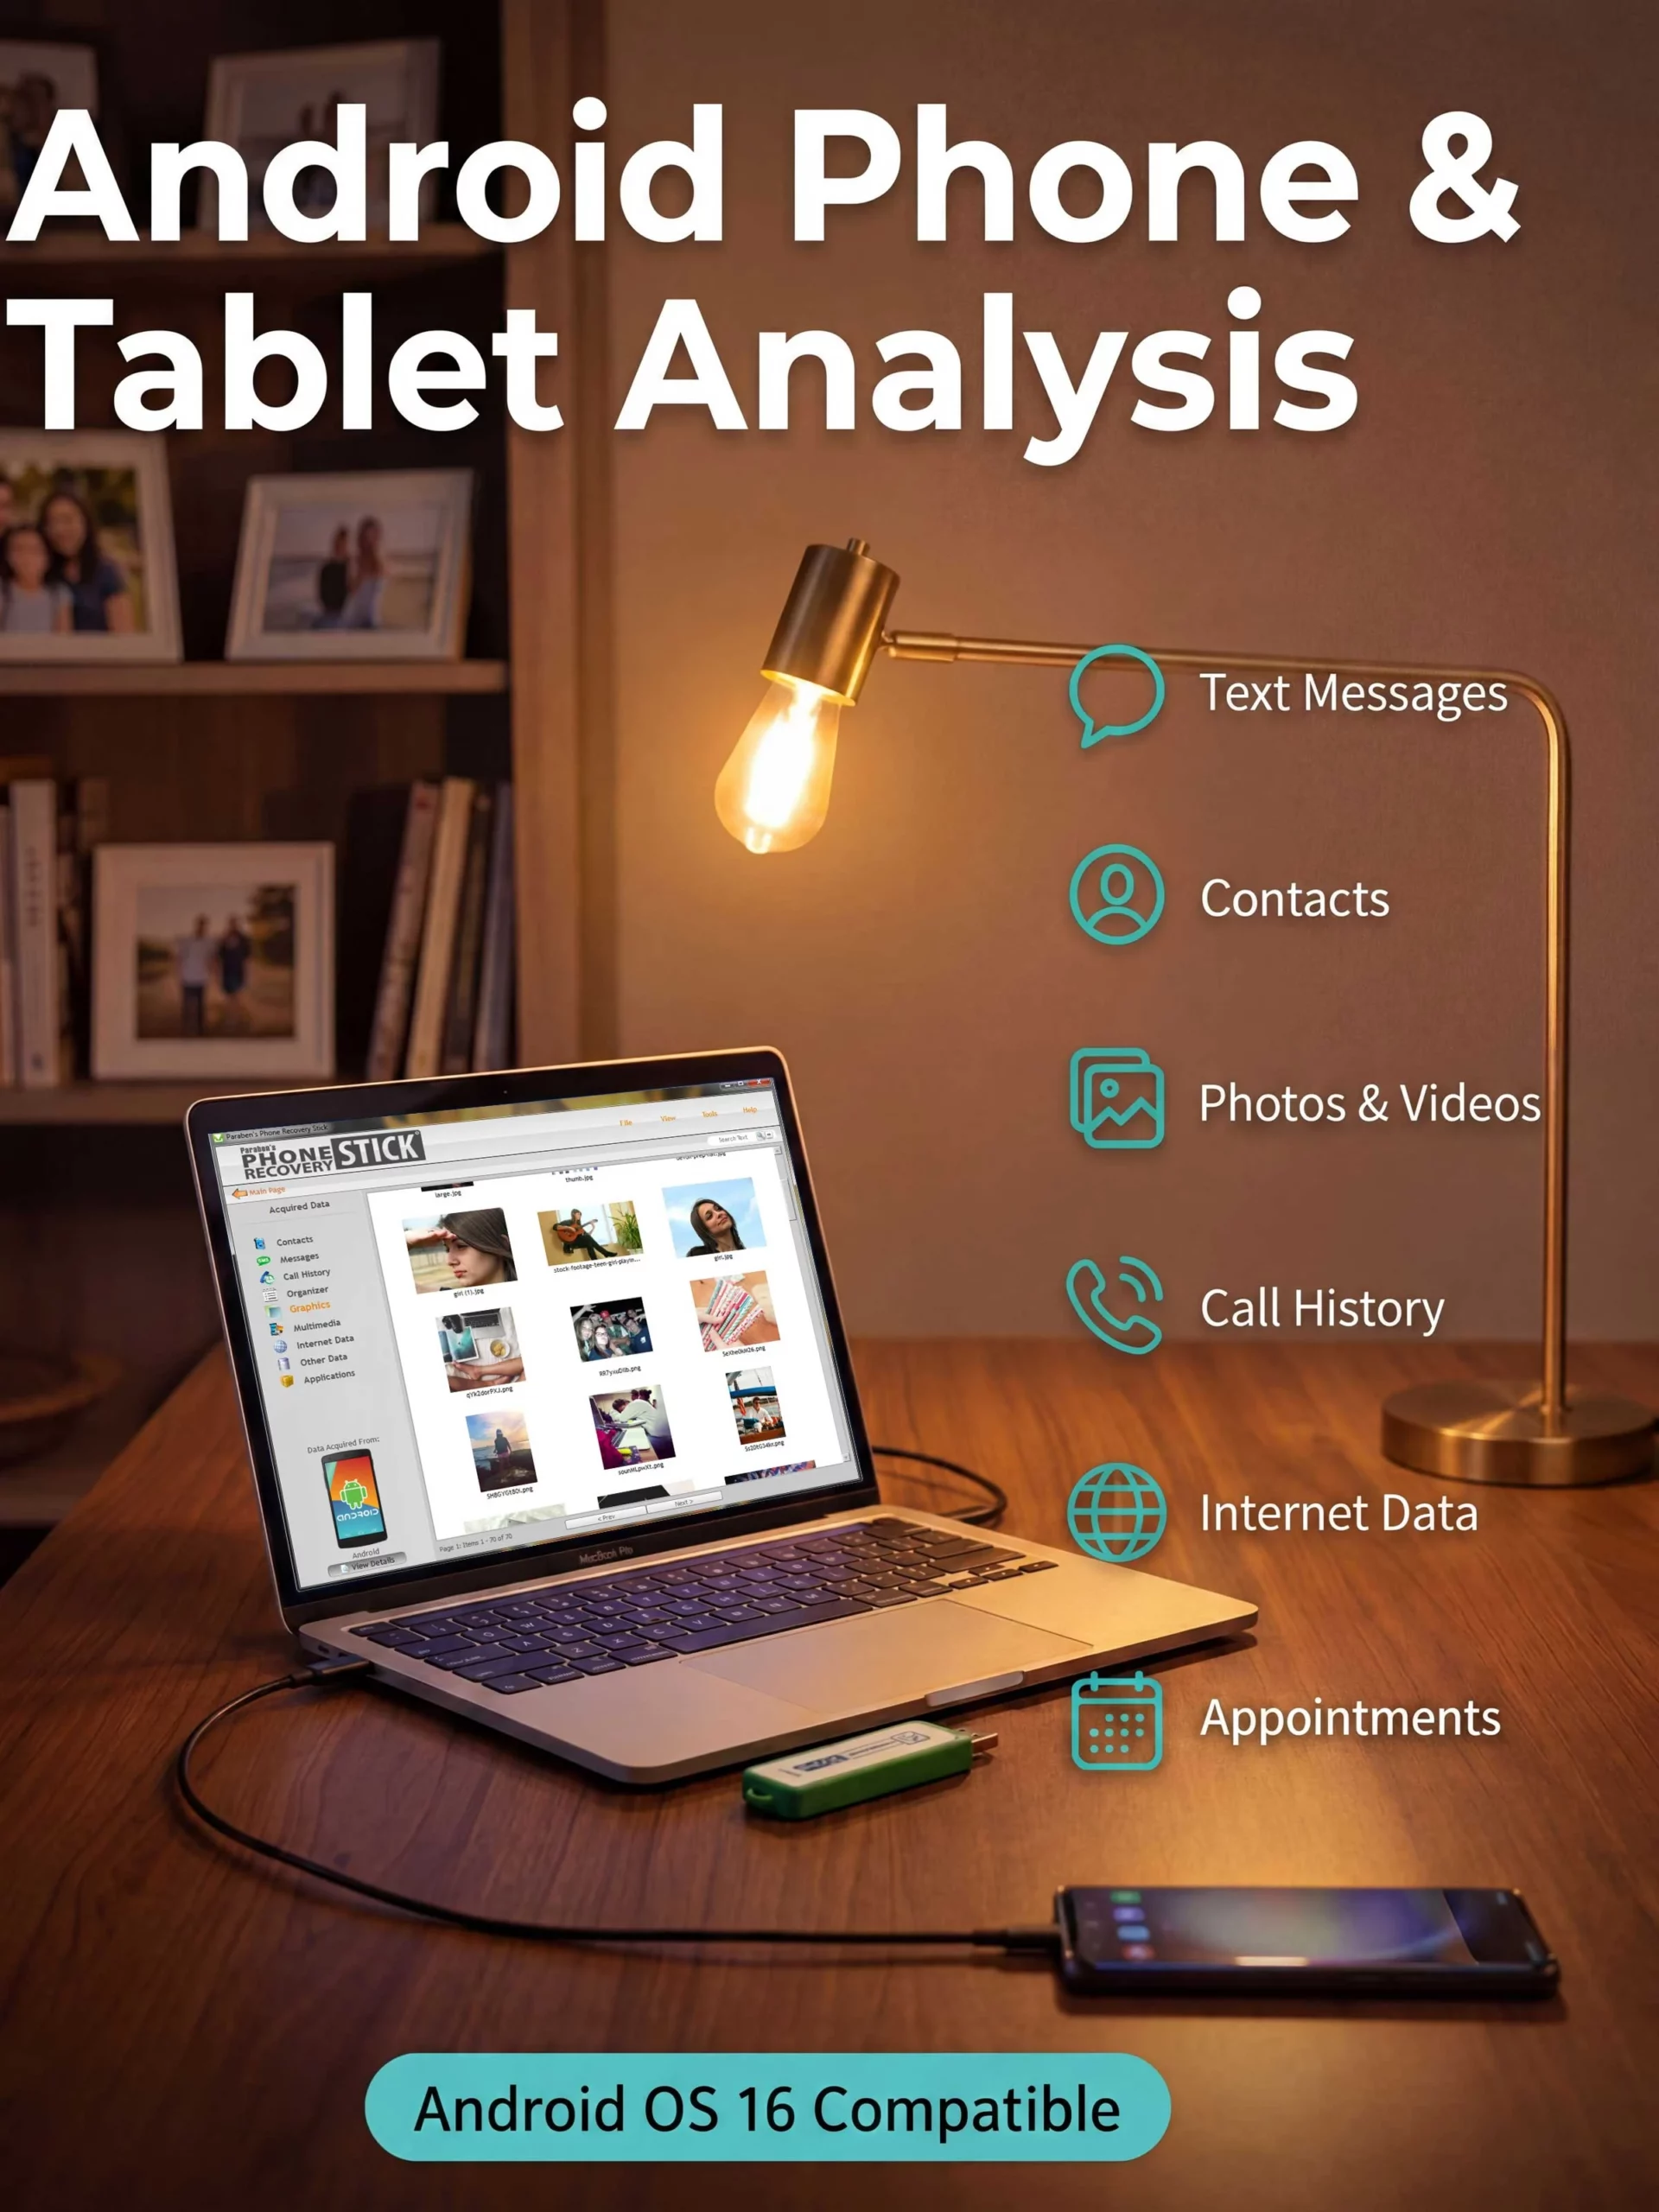
The Phone Recovery Stick provides a dedicated workflow for supported Android devices and can expose supported data such as communications, contacts, multimedia, browser-related information and other accessible artifacts.
The extent of available data varies by device, Android version, security configuration and authorized access.
SIM / UICC Evidence Investigation
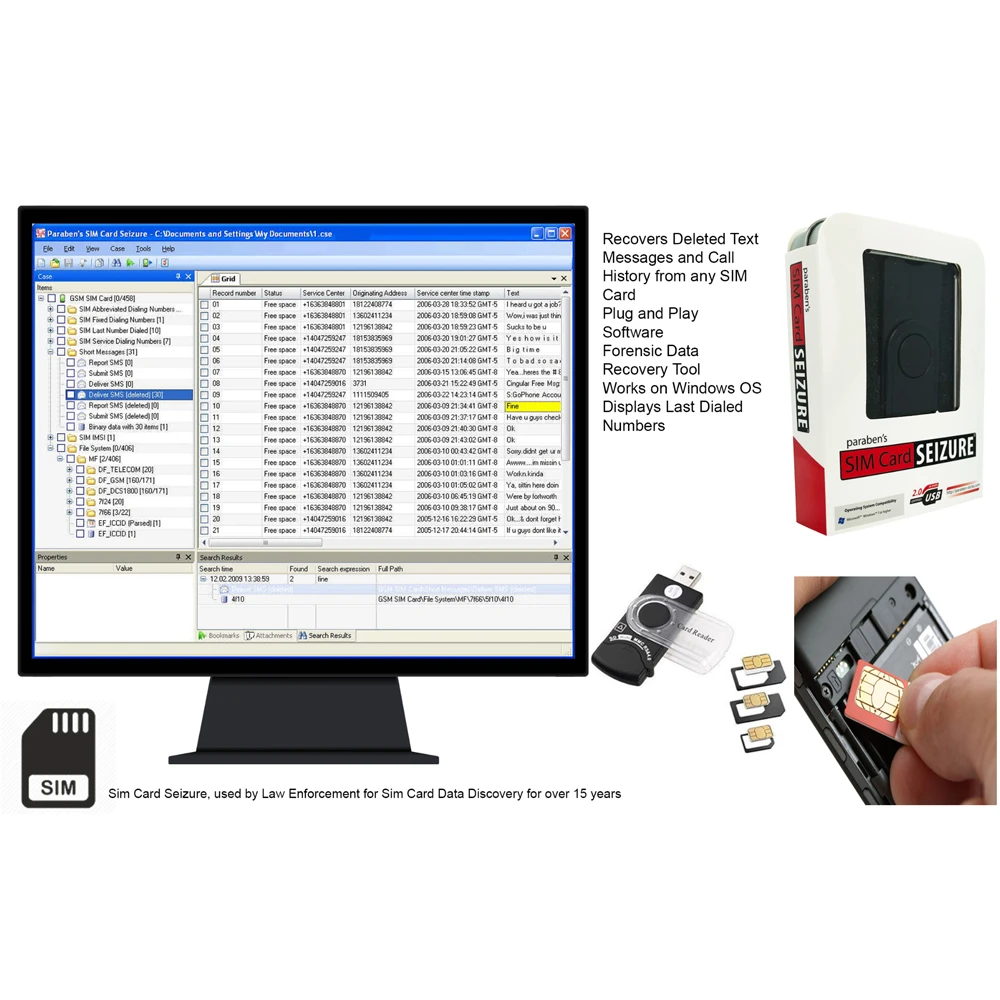
The SIM Card Seizure tool provides a dedicated workflow for examining data stored on supported SIM cards.
Potential evidence sources include:
- SIM-resident contacts
- SMS stored on the SIM
- Call records stored on the SIM
- Last-dialed information
- Other supported SIM-resident information
SIM-resident evidence should not be confused with the complete contents of a modern smartphone. Many contemporary devices store communications and other data internally rather than on the SIM card.
This makes SIM investigation a distinct evidence-source workflow rather than a substitute for mobile-device acquisition.
Windows Data Recovery & Computer Investigation
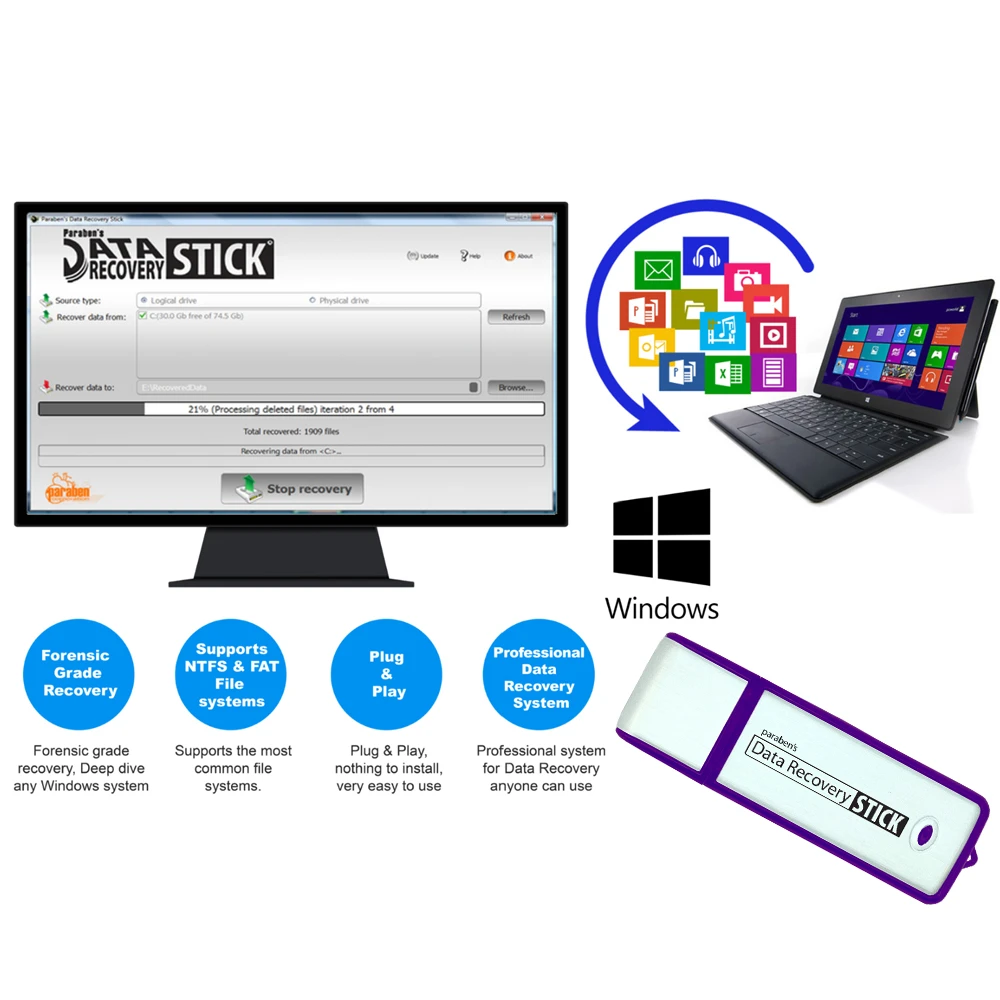
The Data Recovery Stick provides targeted recovery of accessible deleted or inaccessible files from supported Windows storage environments.
Potential recovery targets include:
- Documents
- Photographs
- Video
- Music
- Email-related files
- Web-related data
- Other supported file types
Recovery results depend on filesystem condition, overwriting, fragmentation, storage health and other technical factors.
This is targeted data recovery rather than a claim of complete forensic acquisition of a Windows system.
Digital Media Duplication & Evidence Offloading
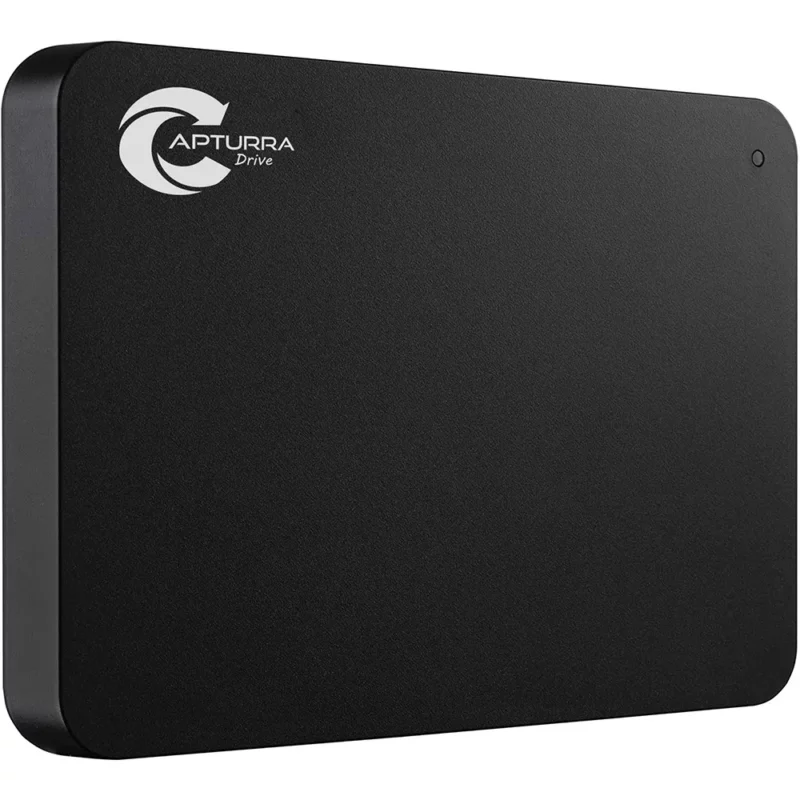
The Capturra component provides automated duplication and offloading of accessible photographs and video from supported digital devices and storage media.
Typical applications include:
- Digital media evidence collection
- Photo and video evidence offloading
- Smartphone media duplication
- SD card evidence offloading
- Surveillance footage offloading
- Automated multimedia duplication
- Portable case-data storage
The system can organize duplicated material into device-specific folders and help reduce repetitive manual copying during evidence collection.
It should not be treated as a universal forensic imaging platform or as a replacement for validated forensic acquisition procedures.
Digital Media Review & Explicit Content Detection
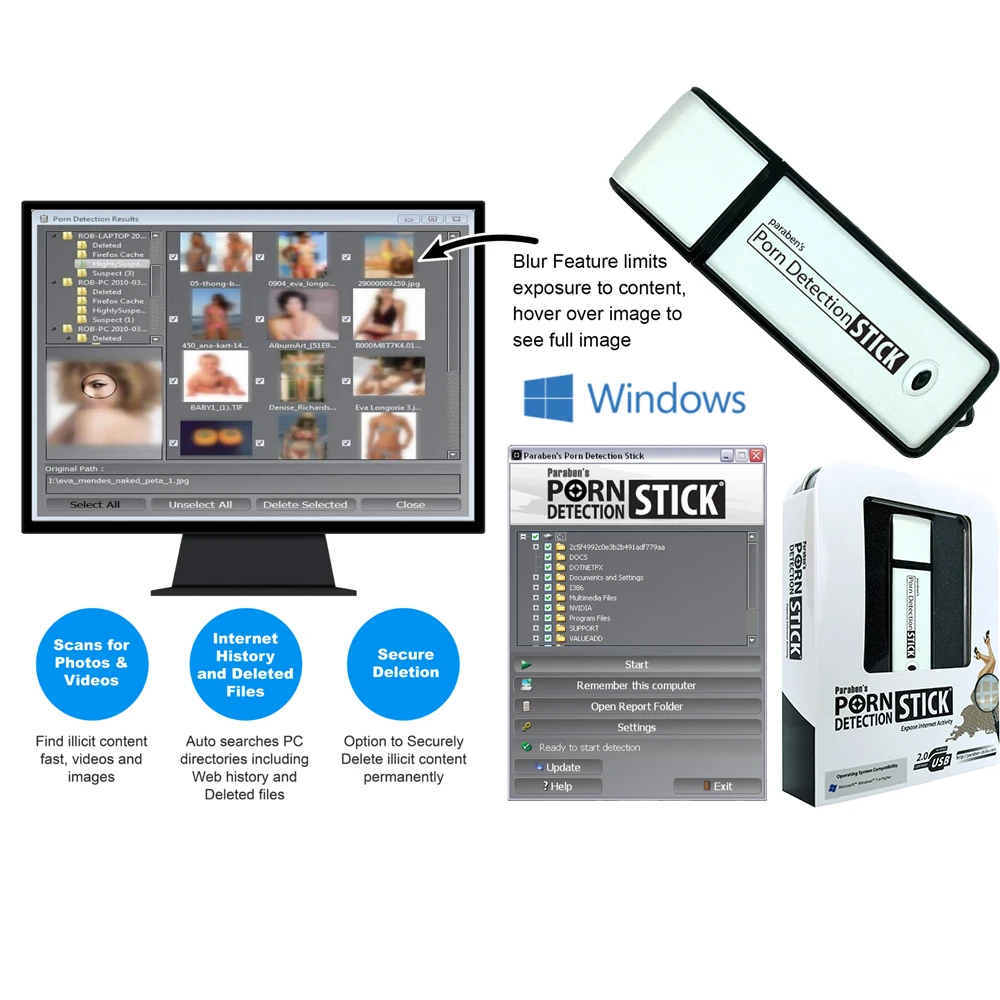
The included content-scanning utility can be used to screen supported Windows storage environments for explicit image and video content.
This can support investigative triage by helping identify files requiring further examination.
Automated content detection should be treated as a screening and review function rather than a final determination of context, ownership, intent or evidentiary significance.
Windows Audio Investigation & Recording
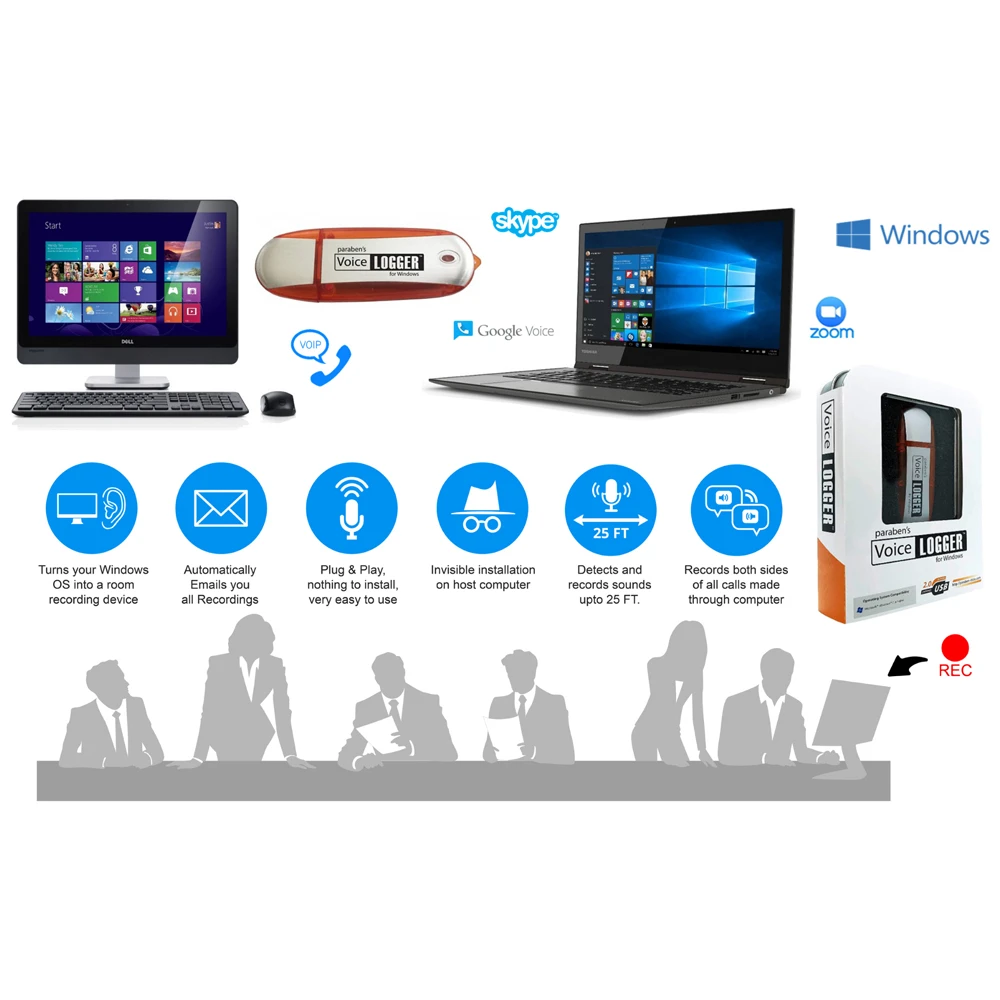
The included Voicelogger software provides Windows-based audio monitoring and recording capabilities for authorized investigative environments.
Potential applications include:
- Windows audio investigation
- Digital audio evidence collection
- Voice-activated recording
- System or microphone audio capture
- Review and export of recorded audio
Audio capture depends on the host computer, available audio interfaces, system configuration and applicable permissions.
Use must comply with applicable law, organizational policy and authorization requirements.
Investigation Workflow
A practical workflow can be structured around the evidence source and investigation objective:
Identify Evidence Source → Establish Authorized Access → Select Appropriate Tool → Collect / Extract / Recover → Consolidate Investigation Data → Review & Analyze → Preserve Relevant Evidence → Continue Formal Examination & Reporting
The kit is therefore best understood as a collection of specialized investigation utilities rather than a single universal forensic engine.
Evidence Handling & Forensic Boundaries
The kit provides tools for collection, extraction, recovery, duplication and investigative review, but these capabilities should not automatically be interpreted as complete forensic acquisition or evidentiary validation.
The available product information does not establish kit-wide functionality for:
- Universal physical or logical forensic imaging
- Hardware write blocking
- Automated hashing across every acquisition workflow
- Integrated chain-of-custody management
- Universal access to protected devices
- Guaranteed recovery of deleted data
- Universal artifact extraction across all device models and operating systems
Organizations conducting formal forensic examinations should apply their own validated procedures for preservation, acquisition, verification, examination, analysis, documentation and chain of custody.
Technical FAQ
What is a complete digital investigation kit?
A complete digital investigation kit combines multiple specialized tools for investigating different digital evidence sources, such as mobile devices, SIM cards, Windows systems and digital media.
What devices can the Complete Digital Investigation Kit investigate?
It is designed around supported iPhone/iPad, Android, SIM/UICC, Windows and digital-media workflows. Actual capability depends on the specific device, operating system, software version, security state and access conditions.
Can the kit extract iPhone and Android data?
Yes, through separate platform-specific tools. The available data depends on device compatibility and authorized access.
Can it recover deleted files?
The Windows Data Recovery component provides targeted file recovery. Recovery of deleted mobile data is conditional and should not be treated as guaranteed.
Is this a complete forensic imaging platform?
No. The kit should not be represented as a universal forensic imaging or acquisition platform. It is a multi-tool investigation and evidence-processing toolkit.
Can it perform SIM card forensic analysis?
It provides a dedicated SIM investigation workflow for supported SIM-resident data, including supported contacts, SMS and call-related records.
Can it duplicate photographs and video from digital devices?
Yes. The Capturra component is designed for automated duplication and offloading of accessible digital media, including supported photographs and video.
Can it investigate surveillance footage?
It can assist with offloading accessible photographs and video from supported surveillance or recording media. This does not make it a dedicated video-forensics platform.
Does the kit include AI?
The manufacturer describes certain components as AI-compatible. This should not be interpreted as a built-in AI forensic engine unless a specific AI model or integrated analysis capability is documented.
Does using the kit automatically establish forensic integrity?
No. Evidence integrity depends on the complete acquisition, preservation, verification and documentation process used by the investigating organization.
Is the kit suitable for law-enforcement and corporate investigations?
Its multi-source architecture can support authorized investigative environments, including law-enforcement, corporate investigation, compliance and digital-risk workflows. Formal evidentiary use should follow the organization’s applicable forensic procedures and validation requirements.
What is the difference between this kit and a mobile forensic kit?
A mobile forensic kit concentrates primarily on mobile devices and related evidence sources. This kit extends beyond mobile investigation to include SIM evidence, Windows data recovery, digital-media duplication, content screening and audio investigation.
Reviews
There are no reviews yet.